Showing posts with label AWS. Show all posts

Monday, May 13, 2024

Setup New Ubuntu 24.0.4 EC2 Instance | How to create EC2 instance in AWS console | Launch Ubuntu 24.0.4 instance in AWS Cloud

How to create Ubuntu 24.0.4 EC2 instance in AWS console?

What is EC2 instance? 

It is virtual server provided by AWS. EC2 instances can be used to setup both Jenkins and Tomcat. Please follow the below steps to create an EC2 instance.

Pre-requisites:

Steps:
1: Login to AWS console by clicking this link -->  https://aws.amazon.com/console/
click on All services, Click on Compute -->  Click on EC2


2. Click on Launch instance


3. Enter Name as EC2 and enter 2 as number of instances (one for Jenkins and another for Tomcat)


4. Select Ubuntu 

5. choose Ubuntu server 24.0.4 as AMI


6. Enter t2.small as instance type
7. Click on Create new Key Pair


8. Choose the existing key pair if you have one already from the drop down, otherwise create new one, give some name as myEC2Key. Make sure you download the key in your local machine. Please do NOT give space or any character while naming the key.


9. Under Network settings, Click Edit


Add port range as 8080 and select AnyWhere as Source Type, that should enter 0.0.0.0/0 as Source

10. Enter 10 GB as storage 
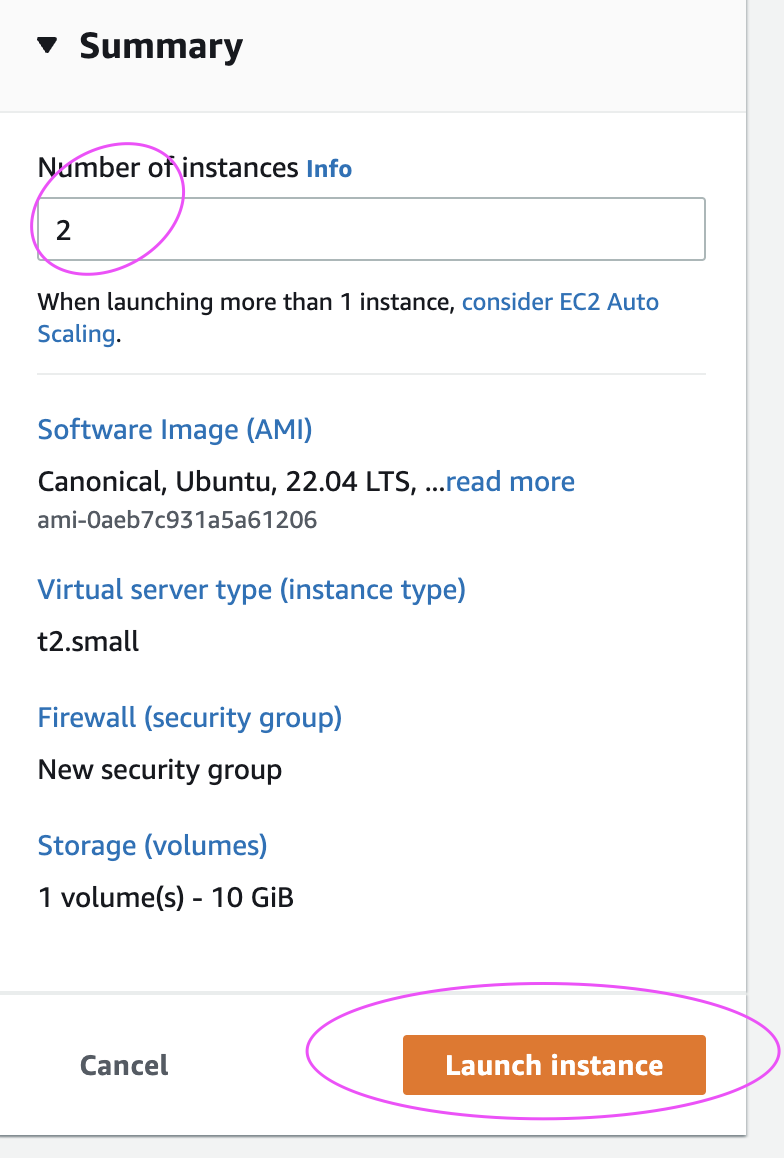
And then make sure in Summary, values appear as below:


11. Click on Launch Instance.

Click on View instances

Now you should be able to view instances in AWS console. Now you can re-name as Jenkins-EC2 and Tomcat-EC2


Watch Steps in YouTube channel:

Connect to EC2 instance from local machine:
Please click the below link to understand the steps for connecting to EC2 instance from your local machine - windows or Apple laptop.

http://www.cidevops.com/2018/02/how-to-connect-to-ec2-instance-from.html


Saturday, April 6, 2024

GitHub Actions CICD Pipeline to Create Docker Image and Push Docker Image into Amazon ECR | Integrate GitHub Actions with AWS ECR

Please find steps for integrating AWS ECR with GitHub Actions:


Pre-requisites:

What are we going to do in this lab?
1. Create a Repository in AWS ECR
2. Create AWS secret keys + access keys
3. Create secrets in GitHub Actions
4. Create workflow yaml
5. Add steps/tasks in the yaml file
6. Run the workflow yaml
7. Check if docker image is been stored in AWS ECR

How to Create a repo in ECR ?

Go to AWS console and search for ECR

Click on Create Repository


Enter name for your repo - all lower case and Click create repository


Once repo is created, choose the repo and click on view push commands. Note down the account ID


Add Access keys and Secret keys as Secrets in GitHub Actions

Go to your GitHub Repo --> Settings --> 

Click on Secrets and Variables under Security in left nav 
Click new Repository Secret


Create secrets in GitHub for AWS_REGION,  REPO_NAME,  AWS_SECRET_ACCESS_KEY and AWS_ACCESS_KEY_ID

Create GitHub Actions CICD workflow yaml:

Go to GitHub repo where your Java project is, create a new file:

.github/workflows/cicd.yml


The below file have four steps(tasks) 
    - Checkout
    - Install Java on runner
    - Build springboot Jar file using Maven
    - Build docker image and tag it
    - Upload docker image into AWS ECR

Copy the content from below:
name: cicd-workflow to create docker image and upload into AWS ECR
on:
  push:
    branches: [ "master" ]
jobs:
  job1:
    runs-on: ubuntu-latest
    steps:
    - uses: actions/checkout@v3
    - name: Set up JDK 17
      uses: actions/setup-java@v2
      with:
        distribution: 'adopt'
        java-version: '17'
    - name: Build with Maven
      run: mvn clean install
    - name: Setup AWS ECR Details
      uses: aws-actions/configure-aws-credentials@v1
      with:
        aws-access-key-id: ${{ secrets.AWS_ACCESS_KEY_ID }}
        aws-secret-access-key: ${{ secrets.AWS_SECRET_ACCESS_KEY }}
        aws-region: ${{secrets.AWS_REGION}}
    - name: Login to Amazon ECR
      id: login-pf-aws-ecr
      uses: aws-actions/amazon-ecr-login@v1
    - name: Build and push Docker image
      env:
        ECR_REGISTRY: ${{ steps.login-pf-aws-ecr.outputs.registry }}
        ECR_REPOSITORY: ${{secrets.REPO_NAME}}
        IMAGE_TAG: ${{ github.sha }}
      run: |
        docker build -t $ECR_REGISTRY/$ECR_REPOSITORY:$IMAGE_TAG .
        docker push $ECR_REGISTRY/$ECR_REPOSITORY:$IMAGE_TAG

Commit the file.

As soon as you commit, build will run immediately in GitHub Actions. 
Now you can see the output of build in Actions tab.


Please login to AWS console --> ECR and verify if image have been uploaded successfully.


Watch Steps in YouTube channel:

Wednesday, August 10, 2022

Create IAM Role with Administrator Access | How to create IAM Role with admin policy

Create IAM Role with Administrator Access

You need to create an IAM role with AdministratorAccess policy.
Go to AWS console, IAM, click on Roles. create a role


Select AWS services, Click EC2, Click on Next permissions.
 
 Now search for AdministratorAccess policy and click


Skip on create tag.
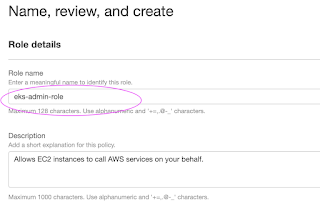
Now give a role name and create it.

Assign the role to EC2 instance
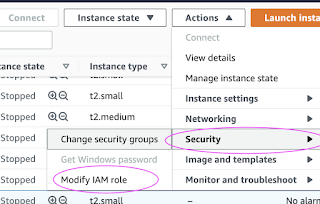
Go to AWS console, click on EC2, select EC2 instance, Choose Security.
Click on Modify IAM Role


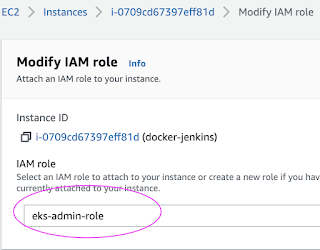
Choose the role you have created from the dropdown.
Select the role and click on Apply.


Create Amazon EKS cluster by Terraform | How to create Amazon EKS cluster in AWS cloud using Terraform | Create EKS Cluster using Terraform

What is Amazon EKS

Amazon EKS is a fully managed container orchestration service. EKS allows you to quickly deploy a production ready Kubernetes cluster in AWS, deploy and manage containerized applications more easily with a fully managed Kubernetes service. Kubernetes is an open-source system for automating deployment, scaling, and management of containerized applications.

EKS takes care of master node/control plane. We need to create worker nodes.

You can create EKS cluster with following node types:
  • Managed nodes -  Linux - Amazon EC2 instances
  • Fargate - Serverless
We will learn how to create EKS cluster based on Managed nodes (EC2 instances).

EKS cluster can be created in following different ways

1. AWS console
2. AWS CLI
3. eksctl command
4. using Terraform

We will create EKS cluster nodes using Terraform.

Pre-requisites:

This Lab is using an EC2 instance with following configured:

Create IAM Role with Administrator Access

You need to create an IAM role with AdministratorAccess policy.
Go to AWS console, IAM, click on Roles. create a role


Select AWS services, Click EC2, Click on Next permissions.
 
 Now search for AdministratorAccess policy and click


Skip on create tag.
Now give a role name and create it.

Assign the role to EC2 instance
Go to AWS console, click on EC2, select EC2 instance, Choose Security.
Click on Modify IAM Role


Choose the role you have created from the dropdown.
Select the role and click on Apply.


Create Terraform files

sudo vi variables.tf

 variable "subnet_id_1" {
  type = string
  default = "subnet-ec90408a"
 }

 variable "subnet_id_2" {
  type = string
  default = "subnet-0a911b04"
 }

 variable "cluster_name" {
  type = string
  default = "my-eks-cluster"
 }

sudo vi main.tf

terraform {
 required_providers {
  aws = {
   source = "hashicorp/aws"
  }
 }
}

resource "aws_iam_role" "eks-iam-role" {
 name = "devops-eks-iam-role"

 path = "/"

 assume_role_policy = <<EOF
{
 "Version": "2012-10-17",
 "Statement": [
  {
   "Effect": "Allow",
   "Principal": {
    "Service": "eks.amazonaws.com"
   },
   "Action": "sts:AssumeRole"
  }
 ]
}
EOF

}

resource "aws_iam_role_policy_attachment" "AmazonEKSClusterPolicy" {
 policy_arn = "arn:aws:iam::aws:policy/AmazonEKSClusterPolicy"
 role    = aws_iam_role.eks-iam-role.name
}
resource "aws_iam_role_policy_attachment" "AmazonEC2ContainerRegistryReadOnly-EKS" {
 policy_arn = "arn:aws:iam::aws:policy/AmazonEC2ContainerRegistryReadOnly"
 role    = aws_iam_role.eks-iam-role.name
}

resource "aws_eks_cluster" "my-eks" {
 name = var.cluster_name
 role_arn = aws_iam_role.eks-iam-role.arn

 vpc_config {
  subnet_ids = [var.subnet_id_1, var.subnet_id_2]
 }

 depends_on = [
  aws_iam_role.eks-iam-role,
 ]
}

resource "aws_iam_role" "workernodes" {
  name = "eks-node-group-example"

  assume_role_policy = jsonencode({
   Statement = [{
    Action = "sts:AssumeRole"
    Effect = "Allow"
    Principal = {
     Service = "ec2.amazonaws.com"
    }
   }]
   Version = "2012-10-17"
  })
 }

 resource "aws_iam_role_policy_attachment" "AmazonEKSWorkerNodePolicy" {
  policy_arn = "arn:aws:iam::aws:policy/AmazonEKSWorkerNodePolicy"
  role    = aws_iam_role.workernodes.name
 }

 resource "aws_iam_role_policy_attachment" "AmazonEKS_CNI_Policy" {
  policy_arn = "arn:aws:iam::aws:policy/AmazonEKS_CNI_Policy"
  role    = aws_iam_role.workernodes.name
 }

 resource "aws_iam_role_policy_attachment" "EC2InstanceProfileForImageBuilderECRContainerBuilds" {
  policy_arn = "arn:aws:iam::aws:policy/EC2InstanceProfileForImageBuilderECRContainerBuilds"
  role    = aws_iam_role.workernodes.name
 }

 resource "aws_iam_role_policy_attachment" "AmazonEC2ContainerRegistryReadOnly" {
  policy_arn = "arn:aws:iam::aws:policy/AmazonEC2ContainerRegistryReadOnly"
  role    = aws_iam_role.workernodes.name
 }

 resource "aws_eks_node_group" "worker-node-group" {
  cluster_name  = aws_eks_cluster.my-eks.name
  node_group_name = "my-workernodes"
  node_role_arn  = aws_iam_role.workernodes.arn
  subnet_ids   = [var.subnet_id_1, var.subnet_id_2]
  instance_types = ["t2.medium"]

  scaling_config {
   desired_size = 2
   max_size   = 2
   min_size   = 1
  }

  depends_on = [
   aws_iam_role_policy_attachment.AmazonEKSWorkerNodePolicy,
   aws_iam_role_policy_attachment.AmazonEKS_CNI_Policy,
   aws_iam_role_policy_attachment.AmazonEC2ContainerRegistryReadOnly,
  ]
 }

Create EKS Cluster with two worker nodes using Terraform

Now execute the below command:
terraform init

This will initialize terraform working directory.
you should see like below screenshot.


Eecute the below command
terraform plan
the above command will show how many resources will be added.

Plan: 10 to add, 0 to change, 0 to destroy.

Now let's create the EKS cluster:

terraform apply


This will create 10 resources.

Update Kube config

Update Kube config by entering below command:

aws eks update-kubeconfig --name my-eks-cluster --region us-east-1

kubeconfig file be updated under /home/ubuntu/.kube folder.

you can view the kubeconfig file by entering the below command:

cat  /home/ubuntu/.kube/config

Connect to EKS cluster using kubectl commands

To view the list of worker nodes as part of EKS cluster.

kubectl get nodes

kubectl get ns

Deploy Nginx on a Kubernetes Cluster
Let us run some apps to make sure they are deployed to Kubernetes cluster. The below command will create deployment:

kubectl create deployment nginx --image=nginx


View Deployments
kubectl get deployments

Delete EKS Cluster

terraform destroy

the above command should delete the EKS cluster in AWS, it might take a few mins to clean up the cluster.

Errors during Cluster creation
If you are having issues when creating a cluster, try to delete the cluster by executing the below command and re-create it.

you can also delete the cluster under AWS console --> Elastic Kubernetes Service --> Clusters
Click on Delete cluster

Sunday, May 1, 2022

Provision Ubuntu 24.0.4 EC2 Instance | How to create EC2 instance in AWS console | Launch Ubuntu 24.0.4 instance in AWS

How to create EC2 instance in AWS console using new UI experience?

What is EC2 instance? 

It is virtual server provided by AWS. We will be using this EC2 to setup both Jenkins and Tomcat. Please follow the below steps to create an EC2 instance.

Watch here for live demo:

Steps:
1: Login to AWS console by clicking this link -->  https://aws.amazon.com/console/
click on All services, Click on Compute -->  Click on EC2


2. Click on Launch instance


3. Enter Name as EC2 and enter 2 as number of instances (one for Jenkins and another for Tomcat)


4. Select Ubuntu 

5. choose Ubuntu server 24.0.4 as AMI


6. Enter t2.small as instance type
7. Click on Create new Key Pair


8. Choose the existing key pair if you have one, otherwise create new one, give some name as myJenkinsKey. Make sure you download the key in your local machine. Please do NOT give space or any character while naming the key.


9. Under Network settings, Click Edit


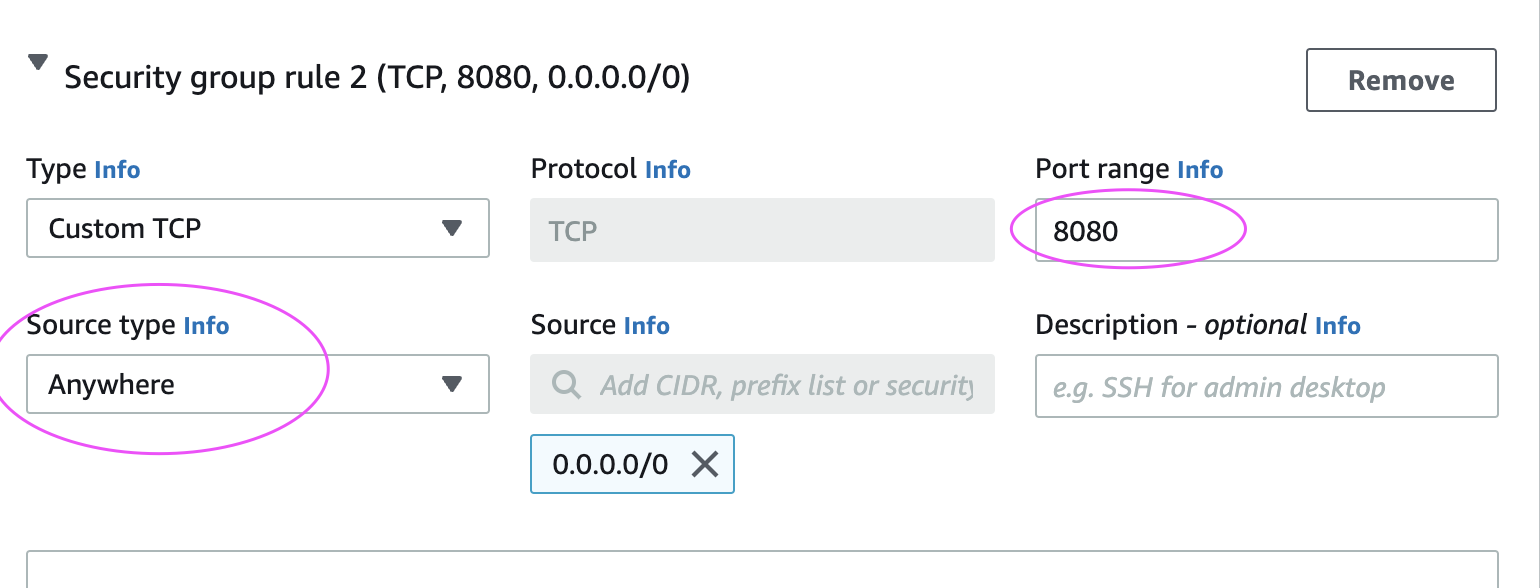
Add port range as 8080 and select AnyWhere as Source Type, that should enter 0.0.0.0/0 as Source

10. Enter 10 GB as storage 
And then make sure in Summary, values appear as below:


11. Click on Launch Instance.

Click on View instances

Now you should be able to view instances in AWS console. Now you can re-name as Jenkins-EC2 and Tomcat-EC2


Connect to EC2 instance from local machine:
Please click the below link to understand the steps for connecting to EC2 instance from your local machine - windows or Apple laptop.

http://www.cidevops.com/2018/02/how-to-connect-to-ec2-instance-from.html

🚀 Live AI-Enabled DevSecOps & Cloud Engineering Bootcamp – Sep 2026

Live AI-Enabled DevSecOps & Cloud Engineering Bootcamp from Coach AK - Sep 2026 Schedule