Showing posts with label IAC. Show all posts

Wednesday, April 16, 2025

What is Checkov? | How to install Checkov on Linux Ubuntu to scan Terraform Code for finding security issues?

Checkov is an open source, static code analysis tool designed to scan Infrastructure as Code (IaC) files and identify potential security and compliance misconfigurations. 

Supported IaC types:

Checkov scans following IaC file types:

  • Terraform (for AWS, GCP, Azure and OCI)
  • CloudFormation (including AWS SAM)
  • Azure Resource Manager (ARM)
  • Serverless framework
  • Helm charts
  • Kubernetes
  • Docker

Here's a breakdown of Checkov tutorials

Getting Started and Basic Usage:

  • Installation: Checkov can be installed using pip, brew, or Docker. For example, using pip:
          sudo apt install python3-pip -y
              sudo pip3 install checkov
    • Basic Scanning: To scan a single file or a directory, use the -f (file) or -d (directory) flags:
      checkov -f main.tf
      checkov -d /path/to/your/iac/code
    • Output: Checkov provides a detailed output of passed and failed checks, including the check ID, description, the resource and file location, and a link to more information about the policy
    • Specifying Frameworks: You can specify the IaC framework to scan using the --framework flag:
             checkov -d /path/to/kubernetes/manifests --framework kubernetes
             checkov -f eks-deploy-k8s.yaml
    • Output Formats: Checkov supports various output formats using the --output flag, such as cli (default), jsonjunitxml, and sarif. For e.g, for JSON output format, use below command:
              checkov -d . --output json


    Saturday, February 10, 2024

    Install Jenkins using Ansible Role on Ubuntu | Install Jenkins using Ansible Role | How to Setup Jenkins using Ansible

    Find below Ansible Role for installing Jenkins on a Ubuntu machine.

    Pre-requisites:
    Java needs to be installed already on machine before setting up Jenkins. please Click here for Java Playbook. Here below is the Ansible Role for installing Jenkins using Ansible in Ubuntu EC2:

    cd ~/roles
    sudo vi aws-infra-role/tasks/installJenkins.yml

    Copy the below yellow highlighted in the above file: 

    ---
        - name: ensure the jenkins apt repository key is installed
          apt_key: url=https://pkg.jenkins.io/debian-stable/jenkins.io-2026.key state=present
          become: yes

        - name: ensure the repository is configured
          apt_repository: repo='deb https://pkg.jenkins.io/debian-stable binary/' state=present
          become: yes

        - name: ensure jenkins is installed
          apt: name=jenkins update_cache=yes
          become: yes

        - name: ensure jenkins is running
          service: name=jenkins state=started


    Modify Hosts/Inventory file
    sudo vi /etc/ansible/hosts
    make sure you add below entry with target node IP changed (in red color).
    [My_Group]  
    xx.xx.xx.xx ansible_ssh_user=ubuntu ansible_ssh_private_key_file=~/.ssh/id_rsa  ansible_python_interpreter=/usr/bin/python3


    Modify Ansible main playbook

    sudo vi aws-infra-role/setup-jenkins.yml
    ---
    # This Playbook creates infra in aws cloud

    - hosts: My_Group
      gather_facts: False
      tags: jenkins creation

      tasks:
      - include: tasks/installJava11.yml
      - include: tasks/installMaven.yml
      - include: tasks/installJenkins.yml

    Execute Ansible Role
    ansible-playbook aws-infra-role/setup-jenkins.yml

    This should install Jenkins on the target node.

    Now enter public ip address or public dns name with port no 8080 of target server by in the browser to see Jenkins up and running.

    http://target_node_public_dns_name:8080

    Tuesday, January 23, 2024

    Create Ansible Role to create a new EC2 instance | Ansible Role for provisioning infrastructure in AWS | Refactor Ansible playbook into Ansible Role

    We will learn how to create Ansible Role for provisioning a new EC2 instance in AWS cloud. We will pick a playbook which has all the logic and we will refactor into reusable ansible role.


    What is Ansible Role?
    Ansible also lets you organize tasks in a directory structure called a Role. Using Ansible roles you can break down complex playbooks into smaller and manageable chunks. Ansible role enables reuse and share our Ansible code efficiently.

    How to create Ansible Role?

    Using ansible galaxy command, we can create Ansible role. This will create the below directory with all the files. 

    directory structure of Ansible role
    aws-infra-role/
    ├── README.md
    ├── create.yml
    ├── defaults
    │   └── main.yml
    ├── handlers
    │   └── main.yml
    ├── meta
    │   └── main.yml
    ├── tasks
    │   ├── create-ec2.yml
    │   └── create-sg.yml
    ├── tests
    │   ├── inventory
    │   └── test.yml
    └── vars
        └── main.yml

    Directory structure explained
    tasks - contains the main list of tasks to be executed by the role.
    handlers - handlers are typically used to start, reload, restart, and stop services.
    defaults - default variables for the role.
    vars - other variables for the role. Vars has the higher priority than defaults.
    meta - defines some data / information about this role (author, dependency, versions, examples, etc,.)

    tests - test cases if you have any.

    Pre-requisites:
    Steps to create EC2 instance using Ansible Role:

    Login to EC2 instance using Git bash or ITerm/putty where you installed Ansible. Execute the below command:

    Create an Inventory file first

    sudo mkdir /etc/ansible

    Edit Ansible hosts or inventory file
    sudo vi /etc/ansible/hosts

    Add the below two lines in the end of the file:
    [localhost]
    local


    cd ~
    mkdir roles  
    cd roles

    Create Ansible Role

    ansible-galaxy role init aws-infra-role


    We will convert this playbook into ansible role.
    So all the variables will go inside vars folder.

    vars
        └── main.yml

    sudo vi aws-infra-role/vars/main.yml
    (copy below content)
    keypair: myNov2023Key
    instance_type: t2.small
    image: ami-007855ac798b5175e
    wait: yes
    group: webserver
    region: us-east-1
    security_group: my-jenkins-security-grp1

    Save the file and come out of it.

    So all the tasks will go inside tasks folder. let's create security group first.

    sudo vi aws-infra-role/tasks/create-sg.yml
    ---
      - include_vars: "vars/main.yml"
        tags: create

    # tasks file for security group
      - name: configuring security group for the instance
        ec2_group:
            name: "{{ security_group }}"
            description: my-ajenkin-security_groAup
            region: "{{ region }}"
            rules:
                - proto: tcp
                  from_port: 22
                  to_port: 22
                  cidr_ip: 0.0.0.0/0
                - proto: tcp
                  from_port: 80
                  to_port: 80
                  cidr_ip: 0.0.0.0/0
                - proto: tcp
                  from_port: 8080
                  to_port: 8080
                  cidr_ip: 0.0.0.0/0
            rules_egress:
                - proto: all
                  cidr_ip: 0.0.0.0/0

    Let's create a task for ec2 instance creation.

    sudo vi aws-infra-role/tasks/create-ec2.yml

    ---
      - include_vars: "vars/main.yml"
        tags: create
      - name: creating ec2 instance
        ec2_instance:
            security_group: "{{ security_group }}"
            name: target-ec2-instance
            key_name: "{{ keypair }}"
            instance_type: "{{ instance_type}}"
            image_id: "{{ image }}"
            region: "{{ region }}"
            wait_timeout: 2   

    Let's create Ansible main playbook.
    sudo vi aws-infra-role/main.yml
    ---
    # This Playbook creates infra in aws cloud

    - hosts: local
      connection: local
      gather_facts: False
      tags: ec2_create

      tasks:
      - include: tasks/create-sg.yml
      - include: tasks/create-ec2.yml

    now execute the ansible playbook by
    ansible-playbook aws-infra-role/main.yml


    If everything is good, you should see the new instance created on AWS console. make sure you are able to connect to that instance.

    That's it!! That is how you create a new EC2 instance using Ansible role in AWS cloud. 
    Please watch steps in YouTube channel:

    Thursday, January 18, 2024

    Ansible Playbook for provisioning a new EC2 in AWS | Create new EC2 instance in AWS cloud using Ansible Playbook

    We will learn how to create a simple Ansible Playbook for provisioning a new EC2 instance in AWS cloud. Please follow the below steps in the machine where you have installed Ansible.

    Pre-requisites:
    Steps to create EC2 instance using Ansible:

    Login to EC2 instance using Git bash or iTerm/putty where you installed Ansible. Execute the below command:

    Create an Inventory file first

    sudo mkdir /etc/ansible

    Edit Ansible hosts or inventory file
    sudo vi /etc/ansible/hosts

    Add the below two lines in the end of the file:
    [localhost]
    local


    cd ~
    mkdir playbooks  
    cd playbooks

    Create Ansible playbook
    sudo vi create-ec2.yml 
    (copy the below content in green color)
    edit the create-ec2.yml to make sure you update the key, AMI and region code which is red marked below:

    - name: Ansible ec2 launch
      hosts: localhost
      connection: local
      gather_facts: False
      tags: provisioning

      vars:
        keypair: myNov2023Key
        instance_type: t2.small
        instance_name: test-ec2-instance
        image: ami-007855ac798b5175e
        wait: yes
        group: webserver
        region: us-east-1
        security_group: my-jenkins-security-grp1

      tasks:
      - name: configuring security group for the instance
        ec2_group:
            name: "{{ security_group }}"
            description: my-jenkins-security_group
            region: "{{ region }}"
            rules:
                - proto: tcp
                  from_port: 22
                  to_port: 22
                  cidr_ip: 0.0.0.0/0
                - proto: tcp
                  from_port: 80
                  to_port: 80
                  cidr_ip: 0.0.0.0/0
                - proto: tcp
                  from_port: 8080
                  to_port: 8080
                  cidr_ip: 0.0.0.0/0
            rules_egress:
                - proto: all
                  cidr_ip: 0.0.0.0/0
      - name: creating ec2 instance
        ec2_instance:
            security_group: "{{ security_group }}"
            name: "{{ instance_name }}"
            key_name: "{{ keypair }}"
            instance_type: "{{ instance_type}}"
            image_id: "{{ image }}"
            region: "{{ region }}"
            wait_timeout: 3

    now execute the ansible playbook by
    ansible-playbook create_ec2.yml


    If everything is good, you should see the new instance created on AWS console. make sure you are able to connect to that instance.

    That's it!! That is how you create a new EC2 instance using Ansible. 

    Watch steps in YouTube channel:

    Thursday, August 24, 2023

    Install Ansible on Red Hat Linux | How to setup Ansible on Red Hat Linux VM | Ansible install on Azure Linux Virtual Machine | Ansible Azure Integration

    How to setup Ansible on Red Hat Linux VM and Integrate with Azure Cloud?

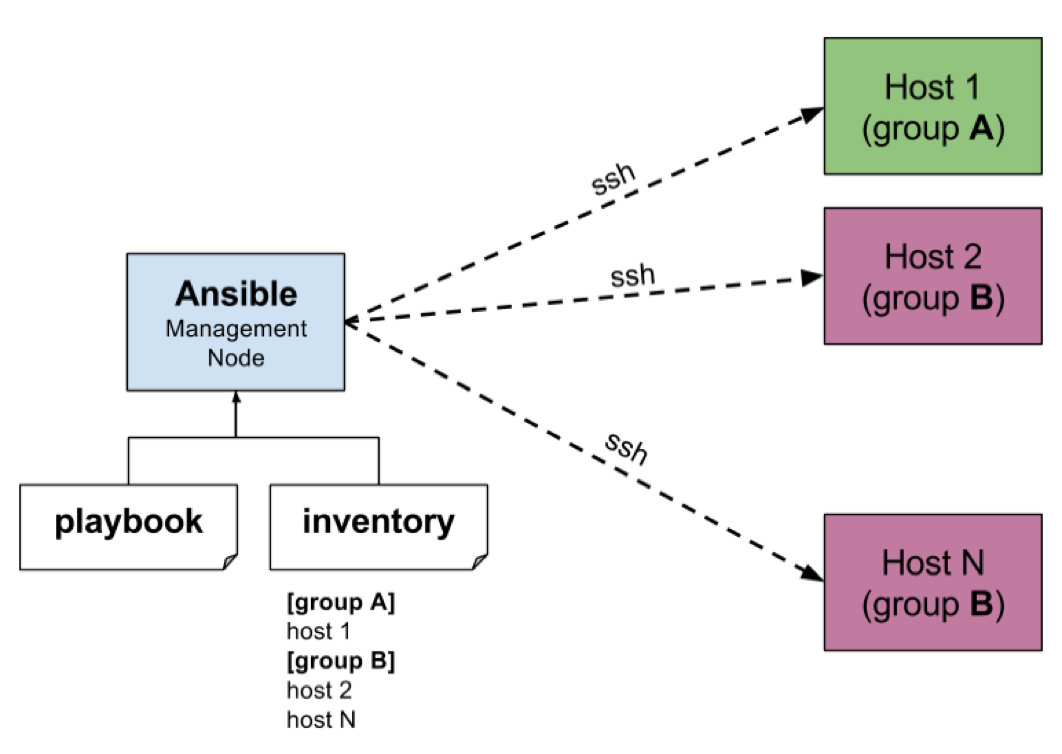
    Ansible is #1 configuration management tool. It can also be used for infrastructure provisioning as well. or You can use Ansible in combination of Terraform which can take care of infra automation and Ansible can do configuration management. We will be setting up Ansible on Red Hat VM in Azure cloud And create some resources in Azure Cloud by using Ansible playbooks.


    Ansible Architecture:
     

    The best way to install Ansible in Linux is to use PIP, a package manager for Python.

    Pre-requisites:
    How to setup Ansible on Red Hat Linux VM

    Watch Steps in YouTube channel:

    Change host name to AnsibleMgmtNode
    sudo hostnamectl set-hostname 
    AnsibleMgmtNode

    Update Repository
    sudo yum update -y

    Install Python-pip3
    sudo yum install python3-pip -y

    Upgrade pip3 sudo pip3 install --upgrade pip


    # Install Ansible pip3 install "ansible==2.9.17"


    check Ansible version
    ansible --version


    # Install Ansible azure_rm module for interacting with Azure.
    pip3 install ansible[azure]

    Authenticate with Azure


    To configure Azure credentials, you need the following information:

    • Your Azure subscription ID and tenant ID
    • The service principal application ID and secret

    Create an Azure Service Principal

    Login to Azure first
    az login
    Enter Microsoft credentials

    Run the following commands to create an Azure Service Principal:

    az ad sp create-for-rbac --name <service-principal-name> \ 
    --role Contributor \ 
    --scopes /subscriptions/<subscription_id>
    Save the above output in a file as you will not be able retrieve later.
    Configure the Ansible credentials using one of the following techniques:

    Option 1: Create Ansible credentials file

    In this section, you create a local credentials file to provide credentials to Ansible. For security reasons, credential files should only be used in development environments.

    mkdir ~/.azure 

    vi ~/.azure/credentials


    Insert the following lines into the file. Replace the placeholders with the service principal values.
    [default] subscription_id=<subscription_id> client_id=<service_principal_app_id> secret=<service_principal_password> tenant=<service_principal_tenant_id>

    Option 2: Define Ansible environment variables

    On the host virtual machine, export the service principal values to configure your Ansible credentials.

    export AZURE_SUBSCRIPTION_ID=<subscription_id> export AZURE_CLIENT_ID=<service_principal_app_id> export AZURE_SECRET=<service_principal_password> export AZURE_TENANT=<service_principal_tenant_id>

    Test Ansible installation

    You now have a virtual machine with Ansible installed and configured!

    This section shows how to create a test resource group within your new Ansible configuration. If you don't need to do that, you can skip this section.

    Option 1: Use an ad-hoc ansible command

    Run the following ad-hoc Ansible command to create a resource group:

    ansible localhost -m azure_rm_resourcegroup -a "name=my-rg123 location=eastus"

    Option 2: Write and run an Ansible playbook

    Create a simple playbook to create resource group in Azure.

    sudo vi create-rg.yml

    ---

    - hosts: localhost

      connection: local

      tasks:

        - name: Creating resource group

          azure_rm_resourcegroup:

            name: "myResourceGroup"

            location: "eastus"

    Execute the playbook using ansible-playbook command.

    ansible-playbook create-rg.yml

    Now Login to Azure cloud to see if the resource group have been created.


    Clean up Resources

    Save the following code as delete-rg.yml

    sudo vi delete-rg.yml

    --- - hosts: localhost tasks: - name: Deleting resource group - "{{ name }}" azure_rm_resourcegroup: name: "{{ name }}" state: absent register: rg - debug: var: rg

    ansible-playbook delete-rg.yml --extra-vars "name=myResourceGroup"

    check in Azure cloud to see if the resource group have been deleted.

    🚀 Live AI-Enabled DevSecOps & Cloud Engineering Bootcamp – Sep 2026

    Live AI-Enabled DevSecOps & Cloud Engineering Bootcamp from Coach AK - Sep 2026 Schedule